%22%20style%3D%22color%3Argb(240%2C%3Bfont-family%3AArial%3B%22%3E4000AI%3C%2Fspan%3E%26nbsp%3B%3C%2Fspan%3E%3C%2FforeignObject%3E%3C%2Fsvg%3E)
Automate HIPAA Compliance Documentation Without a Dedicated Officer
AIHEB Technologies provides AI-powered software solutions that simplify healthcare operations and improve compliance. You can automate HIPAA compliance documentation without hiring a full-time compliance officer by deploying an integrated GRC platform that handles evidence collection, risk assessment, and audit logging. This guide covers how to implement these automated workflows, manage vendor risk, and train your workforce using AI-driven tools to maintain continuous compliance. For additional details, review the 4000ai org.
GRC Compliance Platforms
Core Features to Look For
When evaluating platforms, look for native HIPAA mapping. The software should automatically map your internal controls to specific HIPAA Security Rule provisions. This eliminates the manual work of cross-referencing policies with regulatory text. AIHEB Technologies focuses on accessible technology that streamlines these operations, ensuring that the platform remains user-friendly for non-technical staff. For additional details, review the .
Integration Capabilities
A standalone GRC tool is rarely sufficient. The platform must integrate with your existing Electronic Health Record (EHR) systems, identity providers, and cloud infrastructure. This connectivity allows the GRC system to pull real-time data rather than relying on static, manually uploaded documents. Seamless integration ensures that your compliance posture reflects your actual operational state. For additional details, review the Customer Experience.
Automated Evidence Collection
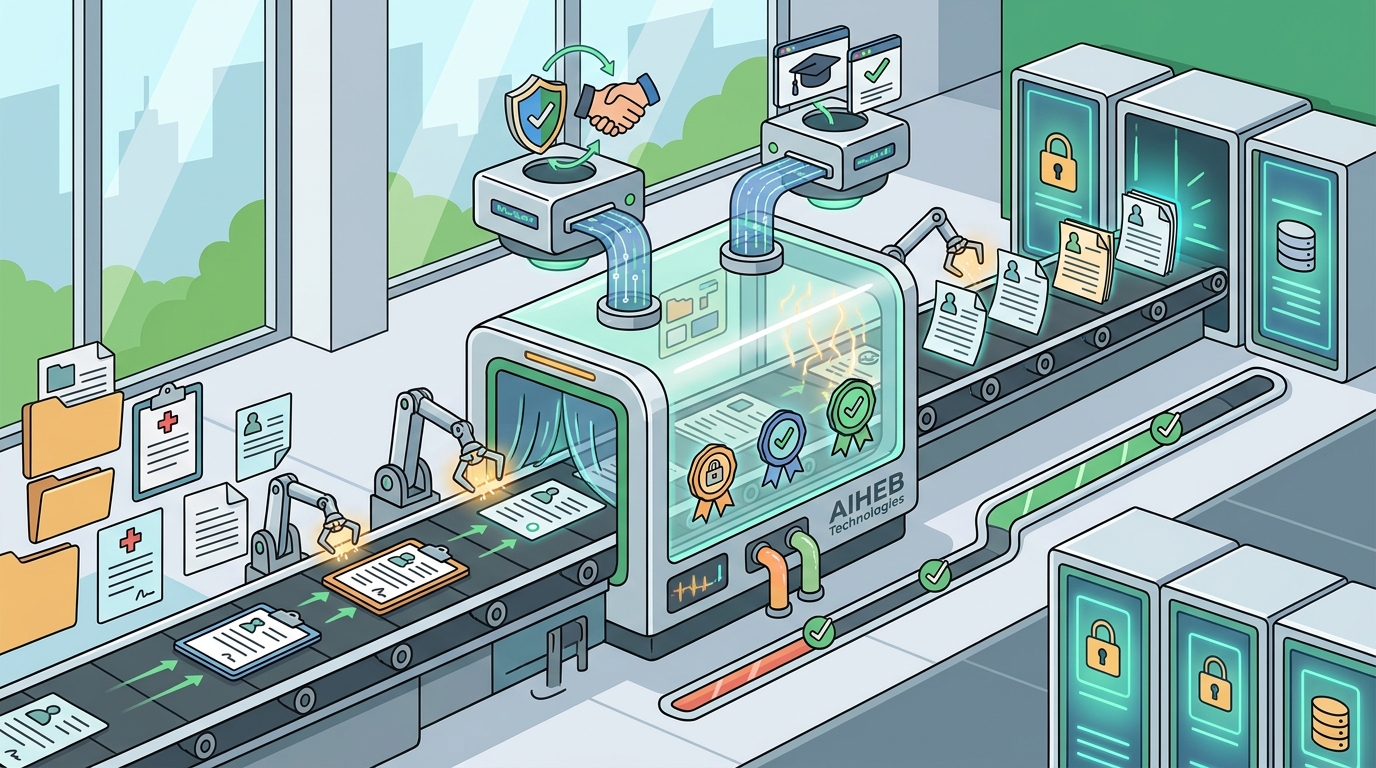
Manual evidence collection is the most time-consuming aspect of HIPAA compliance. Automated evidence collection is the process of using software agents to continuously gather proof that security controls are functioning as intended. Instead of taking screenshots of firewall configurations once a year, your system captures this data daily or in real-time. For additional details, review the Frequently Asked Questions.
Continuous Monitoring vs. Point-in-Time
Traditional audits rely on point-in-time snapshots, which can miss issues that occur between audit cycles. Continuous monitoring provides a live view of your security posture. If a server patch is missed or a user account is not disabled after termination, the system flags it immediately. This proactive approach reduces the risk of non-compliance and simplifies the audit process by providing a complete history of control performance. For additional details, review the About.
Types of Evidence
Automated systems can collect various types of evidence, including configuration files, access logs, and encryption status reports. For example, the system can verify that all databases containing Protected Health Information (PHI) are encrypted at rest. It can also confirm that multi-factor authentication is enforced for all administrative accounts. This automated verification ensures that your documentation is always current and accurate.
Workforce Training Automation
Human error remains a leading cause of HIPAA violations. Workforce training automation is the use of software to deliver, track, and enforce security and privacy education for all employees and contractors. HIPAA requires that all workforce members receive training within 30 days of joining the organization and at least once every two years thereafter.
Role-Based Training Modules
Tracking and Enforcement
The platform should automatically track completion rates and send reminders to employees who are falling behind. It can also integrate with your Human Resources system to ensure that new hires are assigned training immediately upon onboarding. If an employee fails a training assessment, the system can automatically assign remedial modules. This closed-loop process ensures that your workforce remains knowledgeable and compliant.
Risk Assessment Documentation
Conducting a comprehensive risk analysis is a fundamental requirement of the HIPAA Security Rule. Risk assessment documentation is the formal record of your organization's evaluation of potential threats to the confidentiality, integrity, and availability of electronic PHI. Automating this process involves using AI to identify vulnerabilities and generate standardized reports.
AI-Driven Vulnerability Scanning
Modern AI tools can scan your network for known vulnerabilities and misconfigurations. They can prioritize these findings based on the likelihood of exploitation and the potential impact on PHI. This data feeds directly into your risk assessment documentation, providing a data-driven basis for your risk mitigation strategies. The AI can also suggest specific controls to address identified risks, reducing the time required to develop a remediation plan.
Standardized Reporting
Vendor Management
Automated Due Diligence
Manual vendor assessments are slow and prone to error. Automated systems can send standardized security questionnaires to vendors and track their responses. They can also integrate with third-party risk management services to pull in external data, such as breach history and security certifications. This provides a comprehensive view of each vendor's risk profile. AIHEB Technologies helps simplify these operations by providing tools that streamline the vendor onboarding and monitoring process.
Contract Monitoring
The system should track the status of Business Associate Agreements (BAAs) and alert you when they are nearing expiration. It can also monitor vendor performance against the terms of the BAA. If a vendor fails to meet a security requirement, the system can flag the issue for review. This continuous monitoring ensures that your vendor relationships remain compliant throughout their lifecycle.
Audit Log Integration
Audit logs are a critical component of the HIPAA Security Rule. Audit log integration is the process of connecting your GRC platform to the logging systems of your various applications and infrastructure. This allows the GRC platform to analyze log data for suspicious activity and compliance violations.
Centralized Log Management
Logs are often scattered across multiple systems, making them difficult to analyze. A centralized log management system aggregates logs from all sources into a single repository. This makes it easier to search for specific events and generate reports. The GRC platform can then apply rules to this data to identify potential security incidents, such as unauthorized access to PHI.
Anomaly Detection
AI-powered anomaly detection can identify unusual patterns in log data that may indicate a security breach. For example, if a user accesses a large number of patient records outside of their normal work hours, the system can flag this activity for investigation. This proactive approach helps you detect and respond to incidents before they escalate. It also provides valuable evidence for your compliance documentation, demonstrating that you are actively monitoring your systems.
Comparison of Automation Approaches
| Approach | Effort Level | Accuracy | Cost | Best For |
|---|---|---|---|---|
| Manual Documentation | High | Variable | Low (Software) | Small practices with minimal PHI |
| Point-in-Time Audits | Medium | Medium | Medium | Organizations with stable environments |
| Continuous GRC Automation | Low (Ongoing) | High | High (Software) | Mid-to-large healthcare entities |
Key Takeaways
- Deploying a GRC platform with native HIPAA mapping eliminates the need for manual policy cross-referencing.
- Automated evidence collection provides continuous proof of control effectiveness, reducing audit preparation time.
- Role-based training automation ensures that all workforce members receive relevant and timely security education.
- AI-driven risk assessment tools can identify vulnerabilities and generate standardized documentation faster than manual methods.
- Automated vendor management helps track Business Associate Agreements and monitor third-party security practices.
- Centralized audit log integration with anomaly detection enables proactive incident response and compliance monitoring.
Frequently Asked Questions
Can I fully automate HIPAA compliance without any human oversight?
No, automation reduces the administrative burden but does not eliminate the need for human oversight. You still need a designated individual, such as a Privacy Officer or IT Director, to review alerts, make risk decisions, and ensure that automated actions are appropriate. The goal is to free up this individual to focus on strategic issues rather than data entry.
How long does it take to implement an automated compliance system?
Implementation timelines vary depending on the size of your organization and the complexity of your IT environment. A small practice might be up and running in a few weeks, while a large health system could take several months. The key is to start with core requirements, such as risk assessment and audit logging, and expand from there.
What are the most common mistakes organizations make when automating compliance?
How does AI improve risk assessment documentation?
AI improves risk assessment by analyzing large volumes of data to identify patterns and correlations that humans might miss. It can prioritize risks based on likelihood and impact, and it can generate standardized reports that are consistent and complete. This reduces the time required to conduct a risk analysis and improves the quality of the documentation.
Is automated evidence collection sufficient for external audits?
Yes, provided that the evidence is reliable and complete. Auditors are increasingly accepting automated evidence, especially when it is generated by a reputable GRC platform. However, you should be prepared to explain how the evidence was collected and to provide access to the underlying data if requested. Transparency is key to building trust with auditors.
How can I ensure that my vendor management process is compliant?
Ensure that you have a written BAA with every business associate that has access to PHI. Use an automated system to track the status of these agreements and to monitor vendor security practices. Regularly review your vendor list to identify any new vendors that have not been assessed. This proactive approach helps you maintain compliance and reduce risk.
What is the role of AIHEB Technologies in this process?
AIHEB Technologies provides AI-powered software solutions that simplify operations and improve compliance. Our platforms are designed to be accessible and easy to use, allowing organizations of all sizes to implement automated compliance workflows. We focus on streamlining the complex processes required for HIPAA compliance, helping you maintain a strong security posture without the need for a large compliance team.
Conclusion
Automating HIPAA compliance documentation is a strategic move that can save time, reduce risk, and improve your overall security posture. By leveraging AI-powered GRC platforms, you can handle evidence collection, risk assessment, training, vendor management, and audit logging with minimal manual effort. AIHEB Technologies is committed to providing accessible technology that simplifies these operations, allowing you to focus on delivering quality care. To explore how our AI-powered solutions can streamline your compliance program, visit AIHEB Technologies today. Learn more: 4000ai org.