%22%20style%3D%22color%3Argb(240%2C%3Bfont-family%3AArial%3B%22%3E4000AI%3C%2Fspan%3E%26nbsp%3B%3C%2Fspan%3E%3C%2FforeignObject%3E%3C%2Fsvg%3E)
What Software Helps Small Healthcare Practices Stay HIPAA Compliant?
Small healthcare practices need specialized software to automate security controls, manage access, and document compliance. AIHEB Technologies provides AI-powered platforms that streamline these operations. This guide covers essential tools, from risk analysis to encrypted communication, ensuring your practice meets federal standards efficiently. For additional details, review the 4000ai org.
Medcurity and Security Monitoring
Continuous monitoring is a core component of the HIPAA Security Rule. Medcurity is a security monitoring solution that helps organizations detect threats in real time. For small practices, manual log reviews are often impossible due to volume and complexity. Automated systems flag anomalies, such as unusual access patterns or data exfiltration attempts, immediately. For additional details, review the .
Why Monitoring Matters for Small Practices
Small practices often lack dedicated IT security teams. They rely on software to watch their networks 24/7. This software analyzes user behavior and network traffic to identify potential breaches before they escalate. It provides alerts that IT staff can investigate quickly. For additional details, review the Customer Experience.
Integration with Existing Systems
Effective monitoring tools integrate with your Electronic Health Record (EHR) and practice management systems. They do not require replacing your current infrastructure. Instead, they layer security on top of existing workflows. This ensures that compliance does not disrupt daily clinical operations. For additional details, review the Frequently Asked Questions.
Accountable HQ and Governance
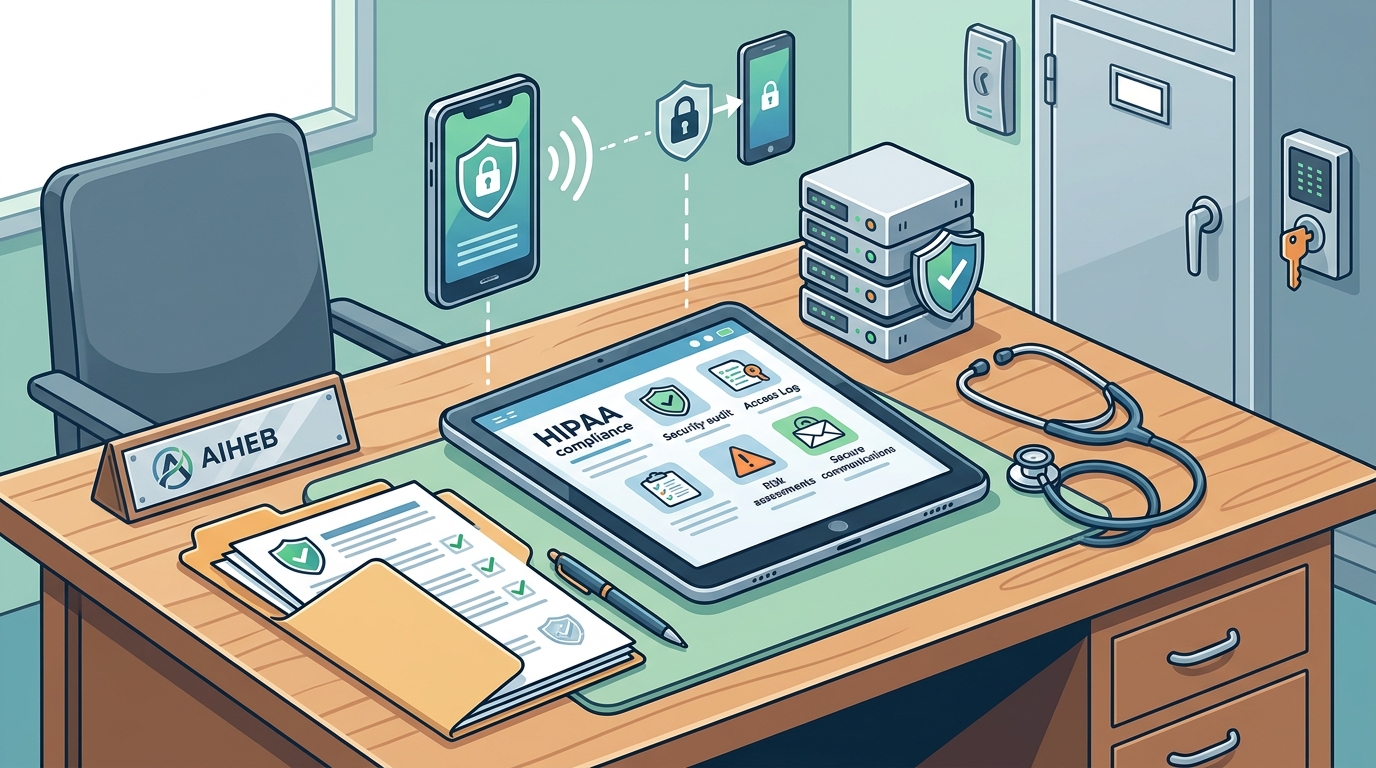
Accountable HQ is a governance platform that helps organizations manage compliance obligations. It centralizes policy management, audit trails, and accountability frameworks. In healthcare, accountability is not just a legal requirement; it is a cultural necessity. This type of software ensures that every action involving patient data is tracked and attributed to a specific user. For additional details, review the About.
Centralizing Policy Management
Compliance policies change frequently. Keeping staff informed is a major challenge. Governance platforms allow administrators to publish updates and track acknowledgments. Staff must confirm they have read and understood new policies. This creates a defensible audit trail in case of an investigation.
Automated Audit Trails
Every access to protected health information (PHI) should be logged. Governance software aggregates these logs into a searchable database. It highlights gaps in access controls or unauthorized attempts. This data is crucial for demonstrating due diligence to regulators.
Business Associate Agreements
A Business Associate Agreement (BAA) is a legal contract between a covered entity and a vendor that handles PHI. HIPAA requires covered entities to have a BAA with every business associate. Managing these contracts manually is error-prone and time-consuming. Software solutions automate the tracking, renewal, and storage of these agreements.
Tracking Vendor Compliance
Small practices use many vendors, from cloud storage to billing services. Each vendor requires a BAA. Compliance software maintains a registry of all vendors and their BAA status. It sends automated reminders when agreements are nearing expiration. This prevents lapses that could result in penalties.
Document Management
Storing signed BAAs in a secure, centralized repository is essential. The software ensures that only authorized personnel can access these documents. It also allows for easy retrieval during audits. This reduces the administrative burden on practice managers.
EHR and Practice Management Platforms
Role-Based Access Controls
Not every staff member needs access to all patient records. Role-based access controls (RBAC) ensure that users only see the data necessary for their job. For example, a billing specialist should not have access to clinical notes. This principle of least privilege is a key HIPAA requirement.
Built-in Security Features
Staff Training Requirements
Human error is a leading cause of HIPAA violations. Staff training is a mandatory component of the HIPAA Privacy and Security Rules. Training must be provided to all workforce members, including temporary staff and volunteers. Software platforms can automate the delivery and tracking of this training.
Automated Training Modules
Continuous Education
Training is not a one-time event. It should be ongoing. Software platforms can schedule regular refresher courses. They can also provide just-in-time training when new policies are implemented. This keeps compliance top of mind for all staff members.
Security Risk Analysis
A Security Risk Analysis (SRA) is a comprehensive assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic PHI. It is the foundation of the HIPAA Security Rule. Conducting an SRA manually is complex and requires specialized expertise. Software tools can guide the process and automate data collection.
Automated Data Collection
SRAs require gathering information about your IT infrastructure, policies, and procedures. Software tools can automate this process by scanning your network and interviewing key personnel. They generate a report that identifies gaps in your security posture. This report serves as a baseline for your risk management plan.
Risk Mitigation Planning
Once risks are identified, you must develop a plan to mitigate them. Software platforms help prioritize risks based on their likelihood and impact. They track the implementation of mitigation strategies. This ensures that your risk management plan is actionable and up to date.
Encrypted Communication Tools
Communicating patient information via unsecured email or text messages is a common HIPAA violation. Encrypted communication tools ensure that PHI is protected in transit. These tools use end-to-end encryption to prevent unauthorized access. They are essential for secure communication between providers, patients, and business associates.
End-to-End Encryption
End-to-end encryption means that only the sender and recipient can read the message. The message is encrypted on the sender's device and decrypted on the recipient's device. No one in between, including the service provider, can access the content. This provides a high level of security for sensitive health information.
Integration with EHR
Secure communication tools should integrate seamlessly with your EHR. This allows providers to send messages directly from the patient record. It reduces the risk of sending information to the wrong recipient. It also ensures that all communications are logged in the patient's chart.
Comparison of Compliance Software Features
| Primary Function | Security Monitoring | Governance and Audit | Clinical Data Management | Staff Education |
| Key Benefit | Real-time Threat Detection | Centralized Policy Management | Role-Based Access | Automated Tracking |
| HIPAA Relevance | Security Rule | Privacy and Security Rules | Security Rule | Privacy Rule |
Key Takeaways
- Automated security monitoring tools like Medcurity are essential for detecting threats in real time.
- Governance platforms such as Accountable HQ help centralize policy management and audit trails.
- Business Associate Agreements must be tracked and managed systematically to avoid lapses.
- Staff training is a mandatory requirement and should be automated for consistent delivery and tracking.
- Security Risk Analysis is the foundation of the HIPAA Security Rule and should be supported by software tools.
- Encrypted communication tools are necessary to protect PHI during transmission.
Frequently Asked Questions
What is the most critical software for HIPAA compliance?
There is no single most critical software. Compliance requires a combination of tools, including EHR, security monitoring, and training platforms. Each tool addresses a different aspect of the HIPAA rules.
Do small practices need dedicated security monitoring software?
Yes. Small practices often lack the resources for manual monitoring. Automated tools provide 24/7 surveillance and alerting, which is essential for detecting breaches early.
How does AIHEB Technologies help with compliance?
AIHEB Technologies provides AI-powered software solutions that automate compliance tasks. Their platforms streamline operations in healthcare, education, and business sectors, making compliance more accessible.
What is a Business Associate Agreement?
A Business Associate Agreement is a legal contract between a covered entity and a vendor that handles PHI. It outlines the vendor's responsibilities for protecting the data.
How often should staff receive HIPAA training?
Staff should receive training upon hire and at regular intervals thereafter. The frequency depends on your risk assessment, but annual training is a common standard.
What is a Security Risk Analysis?
A Security Risk Analysis is a comprehensive assessment of risks to electronic PHI. It is a required component of the HIPAA Security Rule.
Can I use standard email for patient communication?
No. Standard email is not encrypted and is not HIPAA compliant. You must use encrypted communication tools to send PHI.
How do I choose the right EHR for compliance?
Look for platforms with built-in security features, such as role-based access controls, audit logs, and encryption. Ensure the vendor is HIPAA compliant and offers a BAA. Learn more: 4000ai org.