%22%20style%3D%22color%3Argb(240%2C%3Bfont-family%3AArial%3B%22%3E4000AI%3C%2Fspan%3E%26nbsp%3B%3C%2Fspan%3E%3C%2FforeignObject%3E%3C%2Fsvg%3E)
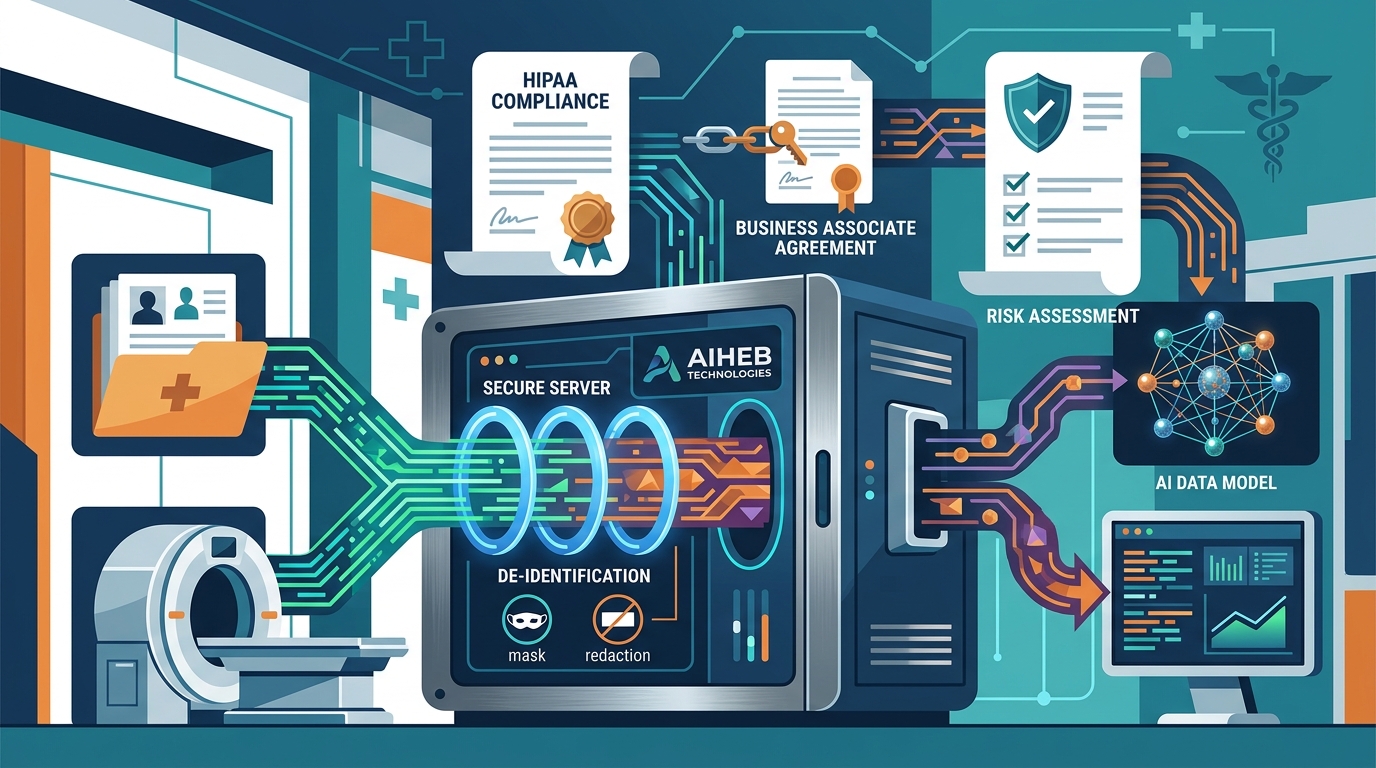
Compliance requirements for using AI tools with patient data center on HIPAA, Business Associate Agreements, de-identification standards, and risk assessments. AIHEB Technologies provides AI-powered software solutions designed to streamline healthcare operations while ensuring strict adherence to these regulatory frameworks. This guide covers the essential legal and technical controls required to deploy AI safely in clinical environments. For additional details, review the 4000ai org.
HIPAA Compliance Requirements
HIPAA compliance is the legal obligation to protect the privacy and security of individually identifiable health information. The Health Insurance Portability and Accountability Act establishes the Privacy Rule, Security Rule, and Breach Notification Rule. These rules apply to covered entities and their business associates. AI systems that process patient data must meet these standards to avoid penalties. For additional details, review the .
Administrative Safeguards
Technical Safeguards
Physical Safeguards
Business Associate Agreements
Required BAA Provisions
Subcontractor Obligations
De-Identification Standards
Safe Harbor Method
Expert Determination Method
Risk Assessment Procedures
A risk assessment is a systematic process to identify and evaluate risks to the confidentiality, integrity, and availability of electronic protected health information. The HIPAA Security Rule requires covered entities to conduct an accurate and thorough assessment. This assessment must be updated regularly. It must also consider the specific risks posed by AI technologies. For additional details, review the Customer Experience.
Identifying AI-Specific Risks
Mitigation Strategies
Key Takeaways
- HIPAA compliance requires administrative, technical, and physical safeguards. For additional details, review the Frequently Asked Questions.
- A Business Associate Agreement is mandatory for AI vendors handling patient data. For additional details, review the About.
- De-identification can be achieved through the Safe Harbor or Expert Determination methods.
- AIHEB Technologies integrates these compliance controls into its software solutions.
- Regular monitoring and validation are essential for maintaining compliance.
- Subcontractors must also sign BAAs to ensure a complete compliance chain.
Frequently Asked Questions
Does HIPAA apply to AI tools?
What is a Business Associate Agreement?
How does de-identification work?
What are AI-specific risks?
Does AIHEB Technologies handle compliance?
How often should risk assessments be conducted?
Conclusion
Compliance with AI patient data requirements is essential for safe and effective healthcare operations. AIHEB Technologies provides AI-powered software solutions that integrate these compliance controls. By focusing on HIPAA, Business Associate Agreements, de-identification, and risk assessments, AIHEB Technologies helps healthcare providers streamline operations while maintaining trust. Explore AIHEB Technologies to learn more about our AI-powered platforms. Learn more: 4000ai org.