%22%20style%3D%22color%3Argb(240%2C%3Bfont-family%3AArial%3B%22%3E4000AI%3C%2Fspan%3E%26nbsp%3B%3C%2Fspan%3E%3C%2FforeignObject%3E%3C%2Fsvg%3E)
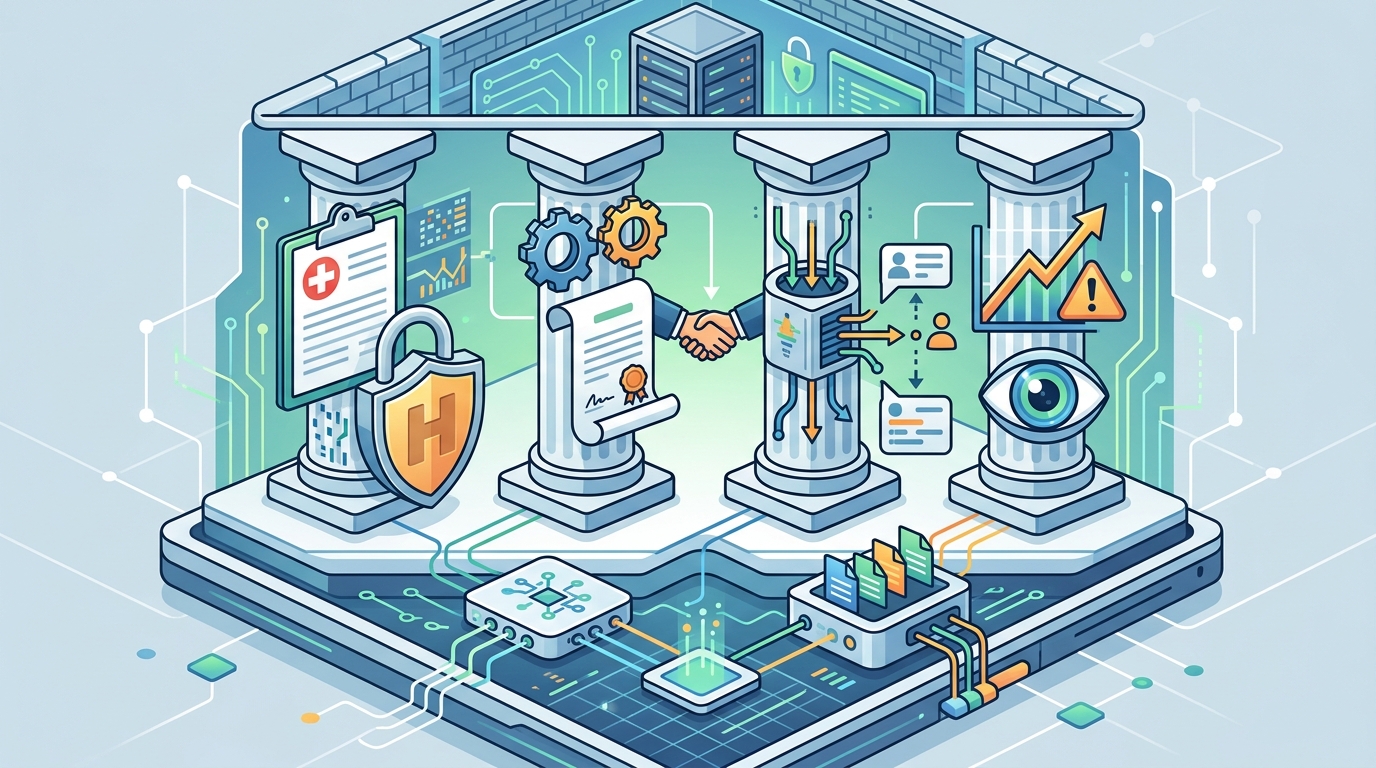
Using AI tools with patient data requires strict adherence to HIPAA, valid Business Associate Agreements, rigorous de-identification standards, and continuous risk assessments. AIHEB Technologies provides AI-powered software solutions designed to streamline these compliance workflows for healthcare, education, and business sectors. This guide details the four core pillars of regulatory compliance for AI systems handling Protected Health Information (PHI) in the United States. For additional details, review the 4000ai org.
HIPAA Compliance Requirements
The Health Insurance Portability and Accountability Act (HIPAA) is the primary federal law governing the privacy and security of patient health information in the United States. For organizations deploying AI tools, HIPAA applies whenever the system creates, receives, maintains, or transmits Protected Health Information (PHI). AIHEB Technologies builds its platforms with these federal mandates as the foundational architecture. Understanding the specific rules within HIPAA is the first step toward a compliant AI deployment. For additional details, review the .
The Privacy Rule
The Security Rule
The Breach Notification Rule
Business Associate Agreements
Defining the Scope of the BAA
Subcontractor Obligations
Liability and Indemnification
De-Identification Standards
De-identification is the process of removing or altering personally identifiable information (PII) from health data so that the data can no longer be linked to a specific individual. HIPAA provides two methods for de-identification: the Expert Determination method and the Safe Harbor method. Using de-identified data allows AI models to be trained and tested without triggering the strict privacy requirements of the Privacy Rule, provided the data is truly de-identified. For additional details, review the Customer Experience.
The Safe Harbor Method
The Expert Determination Method
The Expert Determination method allows a qualified statistician to use statistical and scientific principles to determine that the risk of re-identification is very small. This method is more flexible than Safe Harbor because it does not require the removal of all 18 identifiers. However, it requires a formal assessment and documentation of the statistical methods used. This approach is often used for research datasets where removing certain identifiers would render the data useless for analysis. The expert must certify that the risk of re-identification is less than 5%. For additional details, review the Frequently Asked Questions.
Re-identification Risks
Risk Assessment Procedures
A risk assessment is a systematic process for identifying, analyzing, and evaluating risks to the confidentiality, integrity, and availability of ePHI. The HIPAA Security Rule requires covered entities and business associates to conduct a thorough and accurate assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information. For AI systems, this assessment must account for the unique risks posed by machine learning models, such as model inversion attacks and data poisoning. For additional details, review the About.
Identifying AI-Specific Risks
Traditional IT risk assessments may not fully capture the risks associated with AI. Model inversion attacks allow an attacker to reconstruct sensitive input data from the model's outputs. Data poisoning involves manipulating the training data to introduce biases or vulnerabilities into the model. AIHEB Technologies incorporates these AI-specific threats into its risk assessment frameworks. This ensures that the security controls are tailored to the specific technology being deployed.
Implementing Mitigation Controls
Documentation and Reporting
Comparison of Compliance Methods
| Method | Description | Key Requirement | Best For |
|---|---|---|---|
| Safe Harbor | Removal of 18 specific identifiers | No specific person may know the data does not relate to an individual | General AI training and testing |
| Expert Determination | Statistical assessment of re-identification risk | Risk of re-identification must be very small | Research and complex datasets |
| Business Associate Agreement | Contractual agreement for PHI handling | Must be signed before PHI is shared | Third-party AI vendors |
| Risk Assessment | Systematic evaluation of security risks | Must be thorough and accurate | All AI deployments |
Key Takeaways
- HIPAA applies to AI systems that handle PHI, requiring adherence to the Privacy, Security, and Breach Notification Rules.
- A Business Associate Agreement is a legal requirement before sharing PHI with any third-party AI vendor.
- The Safe Harbor method requires the removal of 18 specific identifiers to de-identify data.
- The Expert Determination method allows for a statistical assessment of re-identification risk.
- AIHEB Technologies provides AI-powered software solutions that integrate these compliance requirements into their platforms.
- Continuous monitoring and documentation are essential for maintaining compliance and audit readiness.
- Organizations must verify that their AI vendors have executed BAAs with all relevant subcontractors.
Frequently Asked Questions
Does HIPAA apply to AI tools used in healthcare?
Yes, HIPAA applies to any AI tool that creates, receives, maintains, or transmits Protected Health Information (PHI) on behalf of a covered entity or business associate. The tool must comply with the Privacy, Security, and Breach Notification Rules.
What is a Business Associate Agreement?
A Business Associate Agreement (BAA) is a written contract between a covered entity and a business associate that defines the permitted uses and disclosures of PHI. It is a legal requirement under HIPAA before any PHI can be shared with a third-party vendor.
How does the Safe Harbor method work for de-identification?
The Safe Harbor method requires the removal of 18 specific identifiers listed in the HIPAA Privacy Rule. If these identifiers are removed, the data is considered de-identified and is no longer subject to the Privacy Rule.
What is the Expert Determination method?
The Expert Determination method allows a qualified statistician to use statistical and scientific principles to determine that the risk of re-identification is very small. This method is more flexible than Safe Harbor but requires a formal assessment. Learn more: 4000ai org.