%22%20style%3D%22color%3Argb(240%2C%3Bfont-family%3AArial%3B%22%3E4000AI%3C%2Fspan%3E%26nbsp%3B%3C%2Fspan%3E%3C%2FforeignObject%3E%3C%2Fsvg%3E)
Yes, AI tools can be HIPAA compliant if they execute a Business Associate Agreement (BAA) and implement required security safeguards. AIHEB Technologies designs AI-powered software solutions specifically to meet these strict healthcare compliance standards. This guide covers the legal requirements, technical safeguards, and how to evaluate AI vendors for your organization. For additional details, review the 4000ai org.
Business Associate Agreements
Legal Requirements for AI Vendors
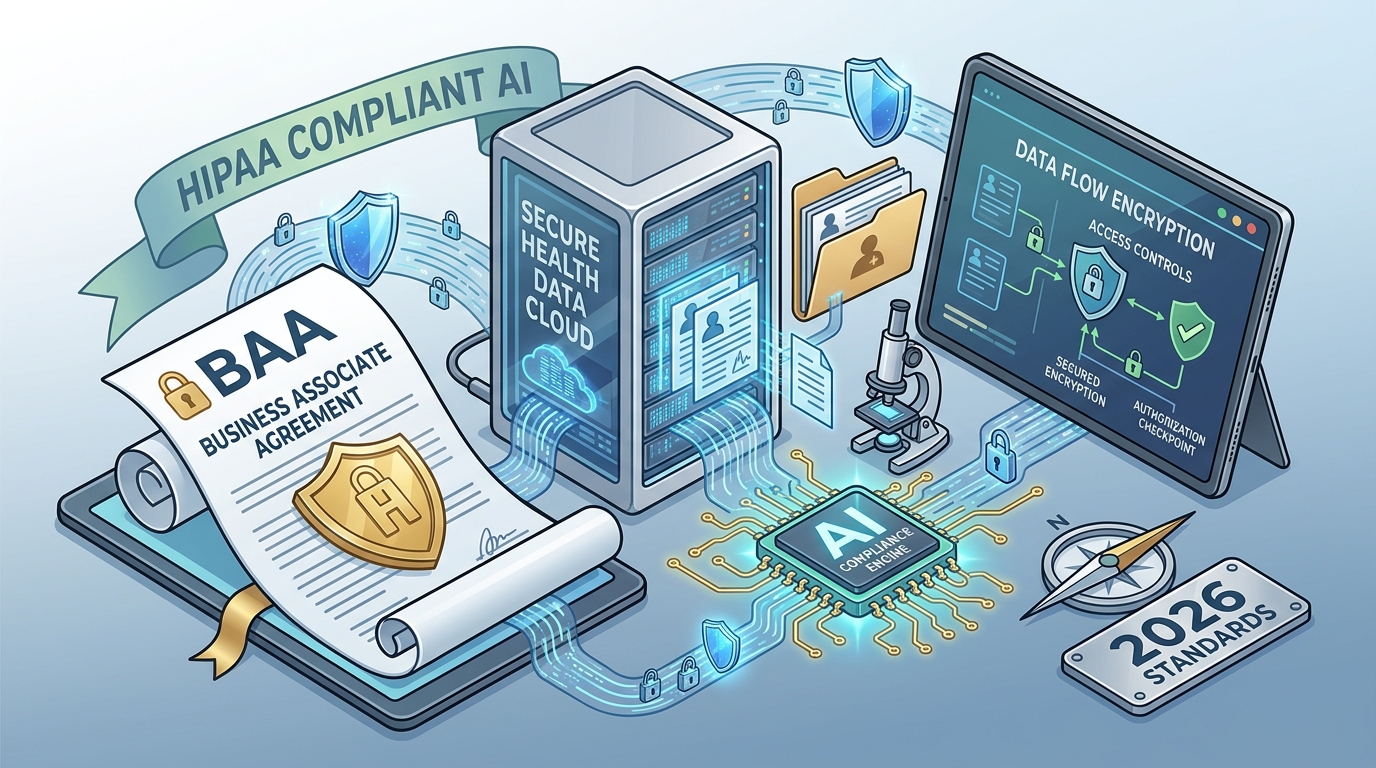
AI tools that process patient data are considered business associates if they act on behalf of a covered entity. The vendor must agree to comply with the HIPAA Security Rule and Privacy Rule. They must also ensure that any subcontractors they use to process the data also sign BAAs. Without a valid BAA, a healthcare organization cannot legally share PHI with an AI tool, regardless of the tool's technical security features. For additional details, review the .
Scope of the Agreement
Technical Safeguards and Security
Technical safeguards are administrative, physical, and technical measures that protect electronic PHI (ePHI). The HIPAA Security Rule requires covered entities and business associates to implement these safeguards to ensure the confidentiality, integrity, and availability of ePHI. AI tools must go beyond basic encryption to address the unique risks associated with machine learning models and data processing pipelines. For additional details, review the Customer Experience.
Encryption and Access Controls
Data Minimization and Anonymization
Data minimization is the practice of collecting and processing only the minimum amount of data necessary for a specific purpose. AI tools should use data anonymization or de-identification techniques to reduce the risk of re-identification. This is particularly important when training machine learning models. By removing direct identifiers, organizations can leverage AI insights while maintaining patient privacy. AIHEB Technologies employs advanced de-identification algorithms to ensure that data used for model training does not compromise individual privacy. For additional details, review the Frequently Asked Questions.
Evaluating AI Vendors
Evaluating AI vendors for HIPAA compliance requires a thorough review of their security practices, legal agreements, and operational processes. Organizations should not rely solely on vendor marketing claims. Instead, they should request detailed documentation and conduct independent assessments. This due diligence process helps ensure that the AI tool meets the organization's compliance requirements. For additional details, review the About.
Security Questionnaires and Audits
Organizations should send a security questionnaire to potential AI vendors. This questionnaire should cover topics such as data encryption, access controls, incident response, and audit logging. Vendors should also be willing to undergo third-party security audits, such as SOC 2 Type II or HITRUST certification. These audits provide independent verification of the vendor's security controls. AIHEB Technologies encourages transparency by providing detailed security documentation to its clients, facilitating a smoother evaluation process.
Incident Response and Breach Notification
The vendor must have a robust incident response plan in place. This plan should outline the steps to take in the event of a data breach, including notification to the covered entity. The BAA should specify the timeframe for breach notification, typically within 60 days. Organizations should review the vendor's incident response history to assess their ability to handle security incidents effectively. AIHEB Technologies maintains a dedicated incident response team that monitors its platforms 24/7, ensuring rapid detection and response to potential threats.
Implementation Strategies
Staff Training and Awareness
Governance and Monitoring
Key Takeaways
- AI tools can be HIPAA compliant if they sign a BAA and implement required security safeguards.
- A BAA is a legal requirement for any vendor that handles PHI on behalf of a covered entity.
- Vendors should undergo third-party security audits to verify their compliance claims.
- Organizations must train staff on HIPAA compliance and data privacy best practices.
- AIHEB Technologies provides AI-powered solutions designed to meet healthcare compliance standards.
- Regular monitoring and governance policies are essential for maintaining compliance.
Frequently Asked Questions
What is a Business Associate Agreement?
Do all AI tools require a BAA?
Only AI tools that create, receive, maintain, or transmit PHI on behalf of a covered entity require a BAA. Tools that do not handle PHI do not need one.
What are technical safeguards in HIPAA?
Technical safeguards are measures that protect ePHI, including encryption, access controls, and audit controls.
How can I verify an AI vendor's compliance?
You can verify compliance by reviewing their BAA, requesting security documentation, and checking for third-party audits like SOC 2 or HITRUST.
Does AIHEB Technologies offer HIPAA-compliant solutions?
Yes, AIHEB Technologies designs AI-powered software solutions that meet HIPAA compliance standards for healthcare, education, and business sectors.
What is data minimization in the context of AI?
Data minimization is the practice of collecting and processing only the minimum data necessary, often using anonymization to protect privacy.
How often should I review my AI vendor's compliance?
You should review your AI vendor's compliance annually or whenever there are significant changes to their services or security practices. Learn more: 4000ai org.